Week in review

AUSCERT Week in Review for 20th November 2026

Greetings, A sophisticated supply chain attack has compromised Optimizely-hosted scripts, allowing threat actors to deliver malicious code to visitors of major web sites, including CNN, the BBC and Zoom. By hijacking trusted third-party infrastructure, the attackers were able to distribute credit card skimmers and iOS-focused exploit kits without directly breaching the affected organisations. The attack was mitigated by some websites by enforcing JavaScript Content Security Policies (CSPs), while many others did not. The incident highlights the growing risk associated with third-party services and website dependencies. Rather than targeting individual companies, cyber criminals can compromise a widely used platform and leverage its trusted position to reach a much larger pool of victims, making supply chain attacks both efficient and difficult to detect. For organisations, the attack serves as a timely reminder that trusted vendors can also become targets. Regular monitoring of third-party scripts, implementing controls such as CSPs, and maintaining strong third-party risk management practices remain critical for reducing exposure to this increasingly common attack vector. FBI warns ARTEX AI hacking tool is powering global cyberattacks Date: 2026-11-15 Author: Bleeping Computer The FBI is warning that hackers are using an AI-powered penetration testing framework called ARTEX to automate cyberattacks against organizations worldwide, including a recent ConnectWise supply-chain breach that compromised Microsoft 365 customer environments. In a FLASH advisory released Friday, the agency said multiple threat actors have weaponized the open-source framework since at least August 2026 to target organizations across the financial, government, technology, defense, healthcare, and other sectors. 2shell2much: NGINX2Root vulnerabilities potentially expose more than 10m websites Date: 2026-11-19 Author: CyberDaily.au Security researchers have uncovered critical vulnerabilities in NGINX, a web server used by more than 80 per cent of Fortune 500 companies. The vulnerability apocalypse is continuing apace, with another batch of newly disclosed vulnerabilities in the NGINX web server revealed overnight, and they are already causing more than a bit of concern among cyber security analysts and practitioners. Dubbed NGINX2Root by researchers at Xint, which helped uncover the flaws, the motley crew consist of five distinct NGINX vulnerabilities and one Linux kernel vulnerability. New NoisyTCP vulnerability lets attackers crash Linux servers Date: 2026-11-16 Author: Bleeping Computer An 11-year-old Linux kernel vulnerability, dubbed NoisyTCP, affects almost all Linux distributions and lets attackers crash systems running Nginx, Apache, and SSH servers with default configurations. According to Hyunwoo Kim, the security researcher who discovered it, this pre-authenticated remote corruption flaw (tracked as CVE-2026-99288) stems from a NULL pointer dereference weakness in the Linux kernel's TCP networking subsystem. Australian retail giant Coles investigates cybersecurity incident Date: 2026-11-16 Author: Bleeping Computer Coles Group Limited, Australia's second-largest retailer, is investigating what it described as a "cyber security incident" that has not impacted the company's stores. Founded in 1914, Coles now employs over 115,000 people, manages a network of more than 1,800 retail outlets, and operates the Flybuys loyalty program with over nine million active members. In a statement issued earlier today, the company said that it's now working with external experts to secure its systems and added that it has yet to find evidence that the attackers stole customer, employee, or supplier data from compromised systems. Oracle to Patch 11 Java Flaws Today as Critical OpenJDK RCE (CVE-2026-114938) Report Emerges Date: 2026-11-17 Author: The Hacker News [See AUSCERT bulletin https://portal.auscert.org.au/bulletins/ASB-2026.0302] Oracle is preparing to release security patches for 11 vulnerabilities in Java SE on Tuesday, November 17, 2026, all of which may be exploited remotely without authentication, as separate reports warn of a potentially critical remote code execution (RCE) flaw affecting OpenJDK. The 11 vulnerabilities carry a maximum CVSS 3.1 severity score of 8.1, according to Oracle's advance security notice. The company has not disclosed their CVE identifiers, affected components, or the individual consequences of exploitation. The separate OpenJDK vulnerability, tracked as CVE-2026-114938, has reportedly been assigned a CVSS 4.0 score of 9.2 and affects OpenJDK 17.0.6 and later. However, those details remain unconfirmed, and there is no evidence yet that the reported flaw is among the 11 vulnerabilities Oracle plans to patch. ASB-2026.0323 – Java4Shell and OpenJDK: CVSS (Max): 8.1 A critical vulnerability in OpenJDK could allow remote code execution through Java4Shell calls. The vulnerability may impact a range of enterprise applications, including Keycloak, Jira, Confluence, Artifactory, Jenkins, and Kafka. ESB-2026.14780 – Splunk Enterprise: CVSS (Max): 10.0 Multiple vulnerabilities affecting bundled third-party components in Splunk Enterprise have been addressed by Splunk through updates to components including OpenSSL, PostgreSQL, MongoDB, Go, gRPC and Traefik. ESB-2026.14683 – BIG-IP APM: CVSS (Max): 9.8 A critical vulnerability in F5 BIG-IP APM could allow an unauthenticated attacker to cause a denial-of-service condition and potentially achieve remote code execution. F5 has released patches to address the issue. ESB-2026.14639 – Tenable Agent: CVSS (Max): 8.2 Tenable has released updates for Tenable Agent to address multiple vulnerabilities in the bundled Expat XML parser library. Users are encouraged to upgrade to the latest version to remediate the affected components. ESB-2026.14667 – WordPress: CVSS (Max): 9.8 WordPress has released a security update addressing multiple vulnerabilities, including privilege escalation, SQL injection, cross-site scripting (XSS), information disclosure, denial of service, and remote code execution issues. Stay safe, stay patched and have a good weekend! The AUSCERT team

Learn more

Blogs

AUSCERT Strengthens Pacific Cyber Security Partnerships

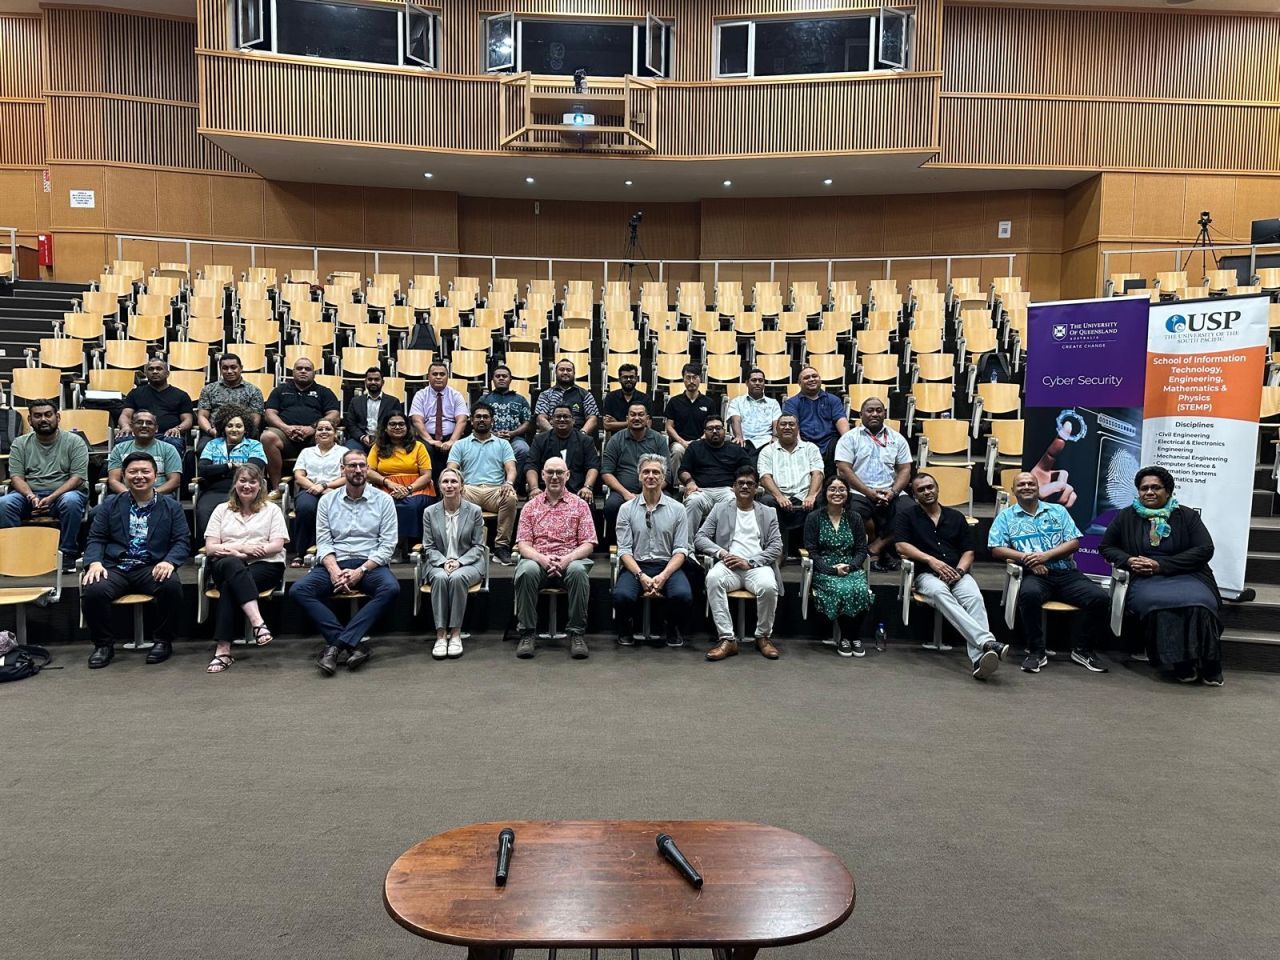
From advancing cyber resilience initiatives to fostering new regional partnerships, a recent visit to Fiji highlighted AUSCERT’s ongoing commitment to strengthening cyber security capability across the Pacific. From 28-31 October, Dr Ivano Bongiovanni, AUSCERT General Manager, visited The University of the South Pacific in Suva, Fiji, to participate in a regional symposium through a collaboration with the UQ Cyber Research Centre, represented by Professor Ryan Ko. During the symposium, Dr Bongiovanni shared insights into emerging challenges in the Governance, Risk and Compliance (GRC) landscape, highlighting the increasing need for practical and sustainable cyber resilience initiatives across the region. He also highlighted AUSCERT’s ongoing contributions to cyber security across the Pacific, including a joint DFAT and IDCARE initiative that helped strengthen cyber resilience among micro-businesses in Fiji and Papua New Guinea, alongside complimentary tabletop exercises delivered to universities in both countries. Beyond the symposium, the visit provided valuable opportunities to engage with academics, researchers, government representatives and industry leaders to discuss how greater collaboration can strengthen cyber resilience throughout the Pacific. Conversations focused on future partnerships, research opportunities and practical initiatives that can help organisations better prepare for an increasingly complex threat landscape. The visit reinforced the importance of regional collaboration in addressing cyber security challenges and further demonstrated AUSCERT’s commitment to sharing knowledge, building capability and supporting a stronger, more resilient cyber security ecosystem across the Pacific.

Learn more

Week in review

AUSCERT Week in Review for 13th November 2026

Greetings, A global widespread outage is affecting Microsoft platforms today with the company confirming a large number of its servers are unexpectedly unavailable triggering the outage. Microsoft is currently investigating the situation and working to restore the platforms. Please be mindful that this will cause interruption or errors on most Microsoft platforms including Outlook, Teams, and SharePoint. As artificial intelligence continues to advance, the Australian Government has proposed a dedicated AI safety regulator to oversee the risks associated with advanced AI models and autonomous agents. The proposal follows a recent incident in which an AI agent accessed public and non-public files linked to a legacy Medicare data portal, highlighting the growing governance and security challenges posed by increasingly capable AI systems. Under the proposed legislation, developers of frontier AI technologies would be required to meet stricter safety obligations, including independent model testing, enhanced risk management, and timely incident reporting. The move aims to strike a balance between innovation, accountability, and the protection of critical systems and sensitive data. Microsoft fixes over 1,000 vulnerabilities in November Patch Tuesday Date: 2026-11-10 Author: CyberScoop [AUSCERT has published security bulletins for these Microsoft updates] Microsoft’s November security update addresses roughly 1,090 vulnerabilities across Windows, Office, Azure and the company’s other product lines, the second consecutive monthly release to exceed the totals of all previous years. The release formally lists 1,094 CVEs, with Windows accounting for 726 and Office 174. A smaller number of patches went to SQL Server, Exchange Server, SharePoint Server, Azure and other products. Citrix, Ivanti Patch Critical and High-Severity Vulnerabilities Date: 2026-11-11 Author: Security Week [See AUSCERT bulletin: https://portal.auscert.org.au/bulletins/ESB-2026.14204/] Citrix and Ivanti on Tuesday announced patches for 19 vulnerabilities in their products, including multiple critical- and high-severity flaws. Ivanti fixed 13 vulnerabilities across five products, including two critical-severity defects in Cloud Services Application (CSA) and Endpoint Manager (EPM). Citrix rolled out fixes for six security defects in XenServer, including CVE-2026-102705, a high-severity bug that could allow attackers to infer the Pool Secret and compromise the host. Critical Zoom Workplace Flaw Could Allow Unauthenticated Remote Privilege Escalation Date: 2026-11-11 Author: The Hacker News [See AUSCERT Bulletins: https://portal.auscert.org.au/bulletins/ESB-2026.14205/ & https://portal.auscert.org.au/bulletins/ESB-2026.14206/] Zoom has released software updates to address two security flaws impacting Zoom Workplace for Windows, including a critical bug that could result in privilege escalation on affected systems. The vulnerabilities are listed below – CVE-2026-108186 (CVSS score: 9.6) – An improper input validation vulnerability that could allow an unauthenticated user to conduct an escalation of privilege via network access. CVE-2026-108187 (CVSS score: 8.1) – An origin validation vulnerability that could allow an unauthenticated user to conduct an escalation of privilege via network access. Hackers Target OpenSSH SSHole Flaw Within Hours of Disclosure, Gain Root on Honeypot Date: 2026-11-06 Author: The Hacker News [See AUSCERT bulletin https://portal.auscert.org.au/bulletins/ASB-2026.0288/] Threat actors are attempting to exploit a recently disclosed security flaw impacting OpenSSH that can enable sign-ins to accounts that have no password set, according to Previdian. The vulnerability, tracked as CVE-2026-123158 (CVSS score: 8.1) and codenamed SSHole (or *sshole), impacts Linux systems that run OpenSSH on the musl C library with Pluggable Authentication Modules (PAM) disabled, including Alpine Linux's default OpenSSH server configuration. Active ScreenConnect attacks breach MSPs, impact dozens of organizations Date: 2026-11-11 Author: Bleeping Computer ConnectWise is investigating an active malware campaign targeting managed service providers (MSPs) that uses compromised ScreenConnect environments to deploy rogue remote-access clients to customer devices. As part of its investigation, ConnectWise has disabled five third-party ScreenConnect extensions across approximately 400 partner environments as a precaution, warning that they may be associated with the attacks. The campaign was first discovered Wednesday by cybersecurity firm Huntress, which says it has identified six compromised MSPs and 286 affected endpoints across 47 organizations, and that the number of victims continues to rise. ASB-2026.0295 – Microsoft Office, Microsoft Office Services and Web Apps: CVSS (Max): 9.9 Microsoft has released update patches to resolve 204 vulnerabilities across several products such as Microsoft 365 Apps for Enterprise, Office LTSC, SharePoint Server and Teams. CVE-2026-124194 has also been listed on the CISA KEV as a known exploited vulnerability. ESB-2026.14056 – Linux kernel (NVIDIA): CVSS (Max): 10.0 Several security issues were discovered in the Linux Kernel that could enable an attacker to compromise the system. A local attacker with hypervisor access could trigger an out-of-bounds condition and compromise the integrity of SEV-SNP guest memory. ESB-2026.14145 – Apple iOS & iPadOS: CVSS (Max): 9.8* Apple released updates for iOS, iPadOS and AirPlay to address vulnerabilities such as accessing sensitive user data, bypassing of rate limits on bluebooth pairing code attempts, corruption of process memory, and joining of iMessage group chats to receive messages. ESB-2026.14206 – Zoom: CVSS (Max): 9.6 Improper Input Validation in Zoom Workplace for Windows may allow an unauthenticated user to conduct an escalation of privilege via network access. Zoom has released update patches to address this vulnerability. ESB-2026.14234 – Adobe Connect: CVSS (Max): 10.0 Adobe has released security updates for Adobe Connect. This update addresses vulnerabilities that could result in privilege escalation, arbitrary code execution, memory exposure, and arbitrary file system read. Stay safe, stay patched and have a good weekend! The AUSCERT team

Learn more
Week in review

AUSCERT Week in Review for 6th November 2026

Greetings, A suspected cyber attack has disrupted supermarkets across Europe, forcing stores to discard large quantities of food after attackers allegedly manipulated refrigeration systems and increased temperatures in fridges and freezers. The incident follows a similar attack on cooling units at hundreds of supermarkets in France just weeks earlier, highlighting the growing cyber risks associated with Internet-exposed operational technology (OT) and Internet of Things (IoT) systems. Dr Ivano Bongiovanni, General Manager of AUSCERT, was interviewed by the ABC, sharing his expert insights on the incident and its implications for Australian businesses. You can listen to the full episode here. This incident serves as a timely reminder that cyber threats extend far beyond traditional IT networks. As organisations continue to adopt smart and connected technologies, securing operational systems is becoming just as critical as protecting corporate networks. When compromised, these systems can lead to significant operational disruption, financial loss, and reputational damage. The attacks underscore the importance of implementing strong cyber security controls, monitoring connected assets, and ensuring operational technology is included in broader cyber resilience and incident response planning. CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key Date: 2026-11-01 Author: The Hacker News A critical flaw in Canonical's LXD and MicroCloud let an attacker log in as a trusted client without holding that client's private key. To do it, the attacker had to reach their HTTPS API over the network and have the trusted client's public certificate. Once in, the attacker would act as that client, with access to the cluster and its virtual machines. If the impersonated account is privileged, the attacker could gain "root access to the host machine," Canonical said. Chrome 157 Rolls Out With 213 Security Fixes, Seven Rated Critical Date: 2026-11-04 Author: Security Week [Please see AUSCERT Bulletin: https://portal.auscert.org.au/bulletins/ESB-2026.13892] Google has promoted Chrome 157 to the stable channel with patches for 213 vulnerabilities, including seven critical memory safety bugs. Google makes no mention of any of these security defects being exploited in the wild, but users should update their browsers as soon as possible. The latest Chrome iteration is now rolling out as versions 157.0.8103.38/.39 for Windows and macOS, and as version 157.0.8103.38 for Linux. CISA says max severity GitLab flaw now exploited in the wild Date: 2026-10-30 Author: Bleeping Computer [See AUSCERT bulletin https://portal.auscert.org.au/bulletins/ESB-2026.12505] Attackers have started exploiting a maximum-severity GitLab vulnerability patched earlier this month, according to the US Cybersecurity and Infrastructure Security Agency (CISA). Tracked as CVE-2026-97229, this critical security flaw was discovered by a security researcher using the 'joaxcar' handle in the CI/CD Regular Expression Compiler, which parses, compiles, and evaluates regular expressions in pipeline configuration files. CVE-2026-97229 stems from an integer overflow weakness and could let remote attackers run arbitrary code on targeted instances via a maliciously crafted regular expression in a CI/CD configuration, due to insufficient expression validation. Debian and Ubuntu APT Flaw Lets Hackers Hijack Software Updates and Execute Code as Root Date: 2026-11-04 Author: Cyber Security News [Please see AUSCERT Bulletins: https://portal.auscert.org.au/bulletins/ESB-2026.13951/ & https://portal.auscert.org.au/bulletins/ESB-2026.13984/] A newly disclosed bug in APT, the package manager behind Debian and Ubuntu, can let a network spy swap a trusted software package for a bad one. The flaw is tracked as CVE-2026-109518 and can end in code running with root rights, the highest level of control on a Linux system. Debian announced the issue on November 4, 2026, and credited researcher Max Justicz with finding it. Drupal Commerce Core Vulnerability Exploited Against Online Stores Date: 2026-10-30 Author: Security Week [AUSCERT has notified potentially affected members about this vulnerability] Drupal says a highly critical Commerce Core access bypass is exploited in the wild and urges store owners to audit their orders. Drupal is urging online store owners to patch a highly critical access bypass vulnerability in the Commerce Core module, warning that it is being exploited in the wild. Tracked as CVE-2026-118539, the issue affects a contributed module that adds e-commerce features to Drupal websites, including a shopping cart and checkout process. Drupal’s statistics show the module is used on more than 42,000 sites. ESB-2026.13725 – IBM QRadar User Behavior Analytics: CVSS (Max): 10.0 Vulnerable components such as framework libraries are susceptible to exploitation with automated tools. User Entity Behavior Analytics App for IBM QRadar SIEM has addressed the applicable CVEs in an update. ESB-2026.13800 – Citrix XenServer: CVSS (Max): 9.8* An unauthenticated attacker on the management network could compromise the host and/or any running Workload Balancing or Conversion Manager applicances. Patches have been released to address these vulnerabilities. ESB-2026.13672 – python-git: CVSS (Max): 9.8 Vulnerabilities in python-git could result in arbitrary command execution, path traversal with arbitrary read/write, config injection, leaking of secrets through environment variable expansion or denial of service. It is recommended to update python-git packages. ESB-2026.13892 – Google Chrome: CVSS (Max): 9.6* Google Chrome has been updated to address 213 security issues in this release. The full comprehensive list of changes and fixes is detailed in the advisory. ESB-2026.13958 – Linux Kernel: CVSS (Max): 10.0 This Linux Kernel update resolves 1077 vulnerabilities, contains two new features and has 11 security fixes. The full comprehensive list of changes and fixes is detailed in the advisory. Stay safe, stay patched and have a good weekend! The AUSCERT team

Learn more
Week in review

AUSCERT Week in Review for 30th October 2026

Greetings, Several major Australian holiday park operators have warned customers about fraudulent emails and messages following a cyber incident affecting booking software provider RMS Cloud. Threat actors reportedly leveraged guest booking information to deliver convincing phishing communications requesting payment and credit card details. The incident highlights the growing risk posed by third-party providers, where a compromise of a trusted supplier can expose customer data and enable highly targeted social engineering attacks. Organisations should use this as a reminder to review supplier risk management processes, strengthen customer communication plans, and ensure staff and customers can identify and conveniently report suspicious requests for sensitive information. A breach doesn't need to occur within your own environment to impact your customers and your reputation. Third-party risk management remains a critical component of cyber resilience. Brotli Decoder Flaw Behind Node.js RCE Also Affects Bun, Python and Other Widely Used Software Date: 2026-10-24 Author: The Hacker News [See AUSCERT Bulletin https://portal.auscert.org.au/bulletins/ASB-2026.0286] A memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, the Python Brotli and brotlicffi packages, and Envoy proxies set up to decompress Brotli. Tracked as CVE-2026-111497, the flaw allows crafted compressed data to overwrite past the end of a buffer and corrupt a program's memory, potentially causing a crash, a memory leak, or the execution of attacker-controlled code. Hackers Target Critical Oracle E-Business Suite RCE Flaw Days After Security Patch Date: 2026-10-28 Author: The Hacker News [AUSCERT has notified potentially affected members via a Critical MSIN. Also, see AUSCERT bulletin: https://portal.auscert.org.au/bulletins/ASB-2026.0261/] Threat actors are beginning to probe for a newly patched critical vulnerability in Oracle E-Business Suite (EBS), according to threat intelligence firm Defused Cyber. The vulnerability in question is CVE-2026-101767 (CVSS score: 9.8) , a case of improper authentication in the Oracle Application Object Library of Oracle E-Business Suite. It was patched by Oracle last week as part of its Critical Patch Update. PHP2Shell security flaws now sucessfully exploited in the wild Date: 2026-10-26 Author: Bleeping Computer [See AUSCERT Bulletin https://portal.auscert.org.au/bulletins/ASB-2026.0252.2] Two critical RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619), collectively tracked as PHP2Shell, have been successfully exploited in the wild. The malicious activity was caught by Adel Karimi, detection and response lead at Perplexity, whose honeypots recorded evidence of confirmed remote code execution against an Apache mod_php installation running PHP 8.4.26. "This is now confirmed RCE with usable memory disclosure, not just a crash followed by a suspicious process. The response delivered an 800 KiB decoded cookie dump, and a function address derived from that dump using the public exploit's offsets appears in the subsequent execution payload," Karimi shared. PHP2Shell Exploitation Hits Government Entity Amid Global Scanning and Signs of AI-Assisted Hacking Date: 2026-10-25 Author: The Hacker News [See AUSCERT Bulletin https://portal.auscert.org.au/bulletins/ASB-2026.0252.2] Threat actors have been observed using agentic artificial intelligence (AI) platforms for post-exploitation activity following the abuse of the PHP2Shell vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619. "In one case, the attackers targeted a government entity in Europe and within two hours of the initial exploitation they had successfully accessed password hashes and multi-factor authentication secrets," Palo Alto Networks Unit 42 said. "They also established an NT LAN Manager (NTLM)-relay tunnel into Active Directory and attempted Domain Admin privilege escalation." Report: Aussie cyber agency received more than 82k cyber crime reports in 12 months Date: 2026-10-27 Author: Cyber Daily The stark new warning is based on the ASD’s seventh Annual Cyber Threat Report, covering the 2025–26 financial year. In that time, the ASD’s Australian Cyber Security Centre (ACSC) fielded over 82,000 cyber crime reports – about one every six minutes. In addition, the agency responded to more than 1,500 cyber security incidents and notified more than 4,400 Australian organisations of potentially malicious activity. ASB-2026.0286 – Brotli Decoder: CVSS (Max): 9.2 A severe memory-corruption vulnerability that exists in Google's reference Brotli decompression library affects a wide array of popular software ecosystems including Node.js, Bun, Envoy, Istio, and Python packages (Brotli and Brotlicffi). Fixed versions have been provided for each affected framework allowing organisations to independently update every impacted runtime or dependency. ESB-2026.13343 – Tenable Network Monitor: CVSS (Max): 9.8 Tenable have provided fixes for Tenable Network Monitor addressing multiple vulnerabilities found in several of their third-party components (OpenSSL, curl, expat, libxml2). ESB-2026.13329 – Apple iOS & iPadOS: CVSS (Max): 8.8 Apple have released software updates to address issues in iOS & iPadOS. Apple recommend applying these updates immediately if possible. ESB-2026.13471 – VMware Cloud Foundation: CVSS (Max): 9.8 Node.js as used in SDDC manager contains a RCE vulnerability due to an out-of-bounds write issue in Brotli decoder. The Broadcom Response Matrix shows that fixed versions for this 'Critical' severity vulnerability are pending. ESB-2026.13388 – Adobe Campaign Classic: CVSS (Max): 10.0 Adobe has released a priority 2 security update for Adobe Campaign Classic. This update addresses critical vulnerabilities that could result in arbitrary code execution, security feature bypass, and privilege escalation. Stay safe, stay patched and have a good weekend! The AUSCERT team

Learn more
Week in review

AUSCERT Week in Review for 23rd October 2026

Greetings, This week, the PHP project released emergency patches for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, collectively known as PHP2Shell. The flaws could allow remote code execution and affect a wide range of PHP deployments, with reports indicating exploitation attempts emerged shortly after disclosure. The Critical vulnerabilities in PHP alert from the Australian Cyber Security Centre (ACSC) warned that all PHP versions from PHP 5 onwards may be affected and urged organisations to identify PHP within their environments, apply available security updates, and monitor systems for suspicious activity. The impact of patching was felt globally, with many web sites temporarily taken offline while remediations were implemented. PHP powers a significant portion of the internet, with estimates of 70% of all web sites running it. This means vulnerabilities in the scripting language can have widespread consequences across the globe. The wave of exploitation activity that has started to emerge is likely to be significant, with many web sites unlikely to be patched. This incident reinforces the importance of maintaining visibility over the software supply chain and applying critical security updates as quickly as possible to reduce exposure to emerging threats. PHP Issues Emergency Patches for Two Critical PHP2Shell RCE Flaws as Exploit Attempts Emerge Date: 2026-10-21 Author: The Hacker News [AUSCERT has notified potentially affected members via a Critical MSIN. Also see AUSCERT Bulletin https://portal.auscert.org.au/bulletins/ASB-2026.0252.2] PHP has released emergency updates that fix two critical flaws in the language itself, letting an attacker without an account run code on a web server. The fixes are in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and the PHP team says only updating fully protects a server. The flaws, together called PHP2Shell, sit in the PHP runtime, not in any application, so a site is exposed even when its own code is secure. The risk is highest on servers using Apache's mod_php, where a working exploit triggers the attack before any application code runs. Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases Date: 2026-10-21 Author: The Hacker News [See AUSCERT bulletin: https://portal.auscert.org.au/bulletins/ESB-2026.13041/] GitLab released fixes on October 21 for a flaw that lets an attacker run code on a self-managed server without logging in, and it affects every version of the software going back to 7.0, released in 2014. The fix matters even for administrators who patched nine days earlier: the October 12 update covered only versions 19.2 and later, and the new fixed versions sit one patch above it, so an instance updated then is in range again. Drupal patches critical RCE flaws, warns exploits may emerge soon Date: 2026-10-17 Author: Bleeping Computer [See AUSCERT bulletin: https://portal.auscert.org.au/bulletins/ESB-2026.12790/] Drupal has patched two critical vulnerabilities that could allow attackers to execute code remotely on websites running any supported version of the content management system. The security issues impact the software core's Field UI module and the contributed Entity List module. Drupal issued an advance warning at the beginning of the week, urging administrators to apply updates promptly because attackers could develop exploits shortly after the vulnerabilities’ disclosure. “The Drupal Security Team urges you to reserve time for core updates at that time because exploits might be developed within hours or days,” the project's security team warned. Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution Date: 2026-10-20 Author: The Hacker News [See AUSCERT Bulletin https://portal.auscert.org.au/bulletins/ESB-2026.12627] Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-106173 (CVSS score: 9.4), is a critical path traversal flaw that could allow an unauthenticated attacker to execute unauthorized code or commands via specially crafted packets. Patches for the flaw were released last week by Fortinet in the following versions – FortiSIEM 7.5.0 (Upgrade to 7.5.1 or above) FortiSIEM 7.6 (Not affected) AdFection: How mercenary spyware invades victims’ devices through targeted advertising Date: 2026-10-15 Author: CyberScoop That online ad you saw for earbuds, a drone or bubble gum-scented car air freshener may have been a gateway for mercenary spyware that can infect your device without you ever having to click on it. The Citizen Lab at the University of Toronto on Thursday said it was revealing the first details of zero-click spyware being delivered through targeted advertising, which it’s calling AdFection. It concluded that while the Israeli company Discover-Tech presents itself as a legitimate advertising firm, in actuality it operates as a facilitator for multiple mercenary spyware partners, including the well-known Candiru. ASB-2026.0252.2 – PHP: CVSS (Max): 9.8 PHP have released updates to address two critical PHP vulnerabilities – CVE-2026-109618 (OOM corruption) and CVE-2026-109619 (stale global state) which allow unauthenticated remote code execution and have been assigned a CVSS score of 9.2 (v4.0) by PHP. ASB-2026.0261 – Oracle E-Business Suite: CVSS (Max): 10.0 Oracle have released a Critical Patch Update that contains 194 new security patches for Oracle E-Business Suite; 31 of these vulnerabilities may be remotely exploitable without authentication ESB-2026.13041 – GitLab Community & Enterprise Edition: CVSS (Max): 10.0 On October 21, 2026, GitLab released updated versions for GitLab Community Edition (CE) and Enterprise Edition (EE). These versions contain important bug and security fixes, and GitLab strongly recommend that all self-managed GitLab installations be upgraded to one of these versions immediately. ESB-2026.13044 – Fortinet Products: CVSS (Max): 9.8 Fortinet have published their advisory on PHP core RCE vulnerability patches (CVE-2026-109618 and CVE-2026-109619). Fortinet is currently investigating the impact of CVE-2026-109618 over Fortinet Products. ESB-2026.13061 – Palo Alto Products: CVSS (Max): 9.2 Palo Alto Networks is aware of two critical vulnerabilities in PHP: CVE-2026-109618 and CVE-2026-109619. Palo Alto Networks is not aware of any malicious exploitation of this issue against their products and will update their advisory with fixed versions and release estimates as they become available. Stay safe, stay patched and have a good weekend! The AUSCERT team

Learn more
Week in review

AUSCERT Week in Review for 16th October 2026

Greetings, The Australian Signals Directorate (ASD) has introduced the ASD Essentials framework, expanding on the long-standing Essential Eight to better address today's diverse technology environments, including cloud, operational technology (OT), and AI-enabled systems. Rather than focusing on a fixed set of controls, the new framework takes a more flexible, outcomes-based approach to cyber resilience. It will be delivered through environment-specific guidance, including Essentials for Enterprise IT, Operational Technology, and Cloud, alongside guidance for executives and AI considerations. Importantly, organisations that have already invested in the Essential Eight do not need to start over. Existing controls remain relevant, and ASD will maintain both frameworks during the transition period. The change signals a shift from treating cyber security as a compliance checklist to focusing on security outcomes and resilience. Now is a good opportunity to review how your current Essential Eight maturity aligns with broader cyber security risks across cloud, OT, and emerging AI technologies. Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories Date: 2026-10-09 Author: The Hacker News Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over 340 repositories. "Using the account of Takashi Kitao, author of the 18,400-star game engine pyxel, the attacker pushed a malicious workflow to 27 repositories starting at 13:20 UTC," StepSecurity said. "Eight hours later, the account of Henry Wu (henrywoo), the original author of Uber's athenadriver, was used to push the same workflow to 318 repositories in a 16-minute window, 21:10–21:26 UTC." GitLab warns of max severity code execution vulnerability Date: 2026-10-12 Author: Bleeping Computer [See AUSCERT Bulletin https://portal.auscert.org.au/bulletins/ESB-2026.12505] GitLab has told users to immediately patch CVE-2026-97229, maximum-severity vulnerability within the CI/CD Regular Expression Compiler, which enables remote code execution (RCE) for threat actors. A specially crafted expression for GitLab's CI/CD Regular Expression Compiler will parse, evaluate, and compile malicious code through the exploitation of a integer overflow weakness. Both Community and Enterprise editions have been patched. Version after 19.2, 19.3, and 19.4 and version before 19.2.8, 19.3.4, and 19.4.2 are vulnerable and should be patched immediately. This vulnerability was reported to GitLab by 'joaxcar' through their HackerOne bug bounty program. Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days Date: 2026-10-13 Author: Bleeping Computer [See AUSCERT Bulletins for Microsoft October Patch Advisories] Today is Microsoft's October 2026 Patch Tuesday, with security updates addressing a record-breaking 1,411 flaws, including one actively exploited and two publicly disclosed zero-day vulnerabilities. This Patch Tuesday addresses 70 "Critical" vulnerabilities, 57 of which are remote code execution, 11 are elevation of privileges, and 2 are spoofing. Palo Alto Networks warns of PAN-OS RCE flaw exploited in attacks Date: 2026-10-14 Author: Bleeping Computer [See AUSCERT bulletin: https://portal.auscert.org.au/bulletins/ESB-2026.12773/] Palo Alto Networks has released security updates for a high-severity PAN-OS RCE zero-day, tracked as CVE-2026-0322, that has been exploited in attacks targeting firewalls. The vulnerability affects the PAN-OS management interface and lets authenticated attackers with network access execute code as root on vulnerable devices. Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch Date: 2026-10-12 Author: The Hacker News Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure. The vulnerability, tracked as CVE-2026-102255 (CVSS score: 10.0), is a case of pre-authenticated server-side request forgery (SSRF) that could allow a remote attacker "to direct the appliance to issue requests on their behalf and reach internal functionality and perform unauthorized operations." Patches for the flaw were released by SonicWall on October 6, 2026, with versions 12.4.3-03670 (platform-hotfix) and 12.5.0-03082 (platform-hotfix). ESB-2026.12605 – Adobe Commerce: CVSS (Max): 10.0 Adobe has released a priority 2 security update for Adobe Commerce. Adobe is not aware of any exploits in the wild for any of the issues addressed in this update. ESB-2026.12505 – GitLab Community & Enterprise Edition: CVSS (Max): 10.0 Updated versions of GitLab Community Edition (CE) and Enterprise Edition (EE) have been released. These versions contain important bug and security fixes, and Gitlab strongly recommends that all self-managed GitLab installations be upgraded immediately. ASB-2026.0251 – Microsoft Windows: CVSS (Max): 9.8 Microsoft has released its monthly security patch updates for the month of October, 2026. This Microsoft Windows update resolves 11125 vulnerabilities and Microsoft recommends updating the software with the version made available on the Microsoft Update Catalogue ESB-2026.12603 – Citrix XenServer: CVSS (Max): 8.8 Citrix have provided security updates that address several issues that affect Citrix XenServer. ESB-2026.12645 – Zoom: CVSS (Max): 8.1 Zoom have provided updates that address an Improper Authorization in Handler for Custom URL Scheme vulnerability in Zoom Workplace for Android. Stay safe, stay patched and have a good weekend! The AUSCERT team

Learn more
Week in review

AUSCERT Week in Review for 9th October 2026

Greetings, Online fashion retailer ASOS has confirmed that customer information may have been accessed following a cyber incident that saw hackers send unauthorised messages through the company's official mobile app. The retailer said names and contact details may have been exposed, while payment card information and account passwords were not affected. The incident came to light after customers received push notifications from the ASOS app containing messages from threat actors claiming responsibility for the attack. ASOS is investigating the incident and working with cybersecurity specialists to secure its systems. Attackers have claimed they stole customer data, although the full scope of the incident remains under investigation and these claims have not been confirmed by the company. The incident highlights the risks associated with third-party communication platforms and trusted customer channels. Even when financial data is not compromised, exposed personal information can be leveraged in phishing and social engineering attacks. Citrix discloses third actively exploited NetScaler zero-day in less than a week Date: 2026-10-05 Author: CyberScoop [See AUSCERT Bulletin https://portal.auscert.org.au/bulletins/ESB-2026.12056/] Citrix customers just got through back-to-back weekends filled with varying levels of uncertainty and worry, as yet another actively exploited zero-day vulnerability was discovered in Citrix NetScaler products. Researchers and security experts said the vulnerability — CVE-2026-88779 — is less concerning because exploitation triggers denial of service and only impacts instances that have SAML (security assertion markup language) enabled. “This means it doesn’t work out of the box against every NetScaler deployment,” Jake Knott, head of threat intelligence at watchTowr, told CyberScoop. “While this is very inconvenient, it doesn’t have organizations scrambling to trigger incident response.” Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users' Mailboxes Date: 2026-10-05 Author: The Hacker News Microsoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges under certain conditions. The vulnerability, tracked as CVE-2026-96940, is rated 8.8 on the CVSS scoring system. "Weak authorization in Microsoft Exchange Server allows an authenticated attacker to elevate privileges over a network," Microsoft said in an advisory released on October 2, 2026. ASOS confirms data breach after “HACKED” in-app notifications Date: 2026-10-06 Author: Bleeping Computer UK fashion retailer ASOS confirmed a data breach Tuesday after hackers sent unauthorized push notifications through its mobile app while claiming to have stolen customer data from the company's Snowflake environment. ASOS is a large UK-based online fashion retailer that sells clothing, footwear, accessories, and beauty products to customers worldwide, including in the United States. Chrome 155 Update Patches 247 Vulnerabilities Date: 2026-10-07 Author: Security Week [See AUSCERT Bulletin https://portal.auscert.org.au/bulletins/ESB-2026.12256] Four critical-severity use-after-free defects were fixed in Chromecast, Browser, Navigation, and Track. Google on Tuesday rolled out a Chrome 155 security update that addresses 247 vulnerabilities, including four critical-severity flaws. All four critical bugs are use-after-free issues. They impact Chrome’s Chromecast, Browser, Navigation, and Track components and are tracked as CVE-2026-106382, CVE-2026-106197, CVE-2026-106358, and CVE-2026-106347. Hackers exploit critical Atlassian flaw after public PoC release Date: 2026-10-07 Author: Bleeping Computer [See AUSCERT Bulletin https://portal.auscert.org.au/bulletins/ESB-2026.12187] A critical vulnerability (CVE-2026-21589) affecting multiple Atlassian product families, including Jira, Confluence, and Bitbucket, is being exploited in attacks that do not require authentication. Earlier today, security company Previdian detected the activity on its honeypot network, just hours after a detailed technical report was published. An unauthenticated attacker can exploit CVE-2026-21589 to access specific files in the application's web root directory if they know the file's exact name and path. ESB-2026.12162 – GitLab AI Gateway: CVSS (Max): 9.9 Updated versions of GitLab Self-Hosted AI Gateway, that contain a critical security fix, have been released. Gitlab strongly recommends that all GitLab Self-Managed customers with GitLab Self-Hosted AI Gateway installations update to one of these versions immediately. ESB-2026.12056 – Citrix NetScaler ADC & Citrix NetScaler Gateway: CVSS (Max): 7.5 Software updates have been released to address a vulnerability in Citrix NetScaler ADC (formerly Citrix ADC) and Citrix NetScaler Gateway (formerly Citrix Gateway). ESB-2026.12246 – Hitachi Energy SOI: CVSS (Max): 8.8 Hitachi Energy is aware of a RCE (Remote Code Execution) vulnerability in the Apache ActiveMQ component of SOI product versions. Users are advised to apply the patch SOI EP2, which upgrades the ActiveMQ version (JMS message broker) for the SOI Core. ESB-2026.12323 – Splunk Enterprise: CVSS (Max): 9.8 Splunk have provided upgrades that address multiple vulnerabilities in Splunk Enterprise. ESB-2026.12333 – Cisco License (Smart Software Manager) On-Prem: CVSS (Max): 10.0 Cisco has released software updates that address vulnerabilities that affect Cisco License On-Prem – regardless of software configuration. Stay safe, stay patched and have a good weekend! The AUSCERT team

Learn more
Week in review

AUSCERT Week in Review for 2nd October 2026

Greetings, October is Cyber Security Awareness Month, and the Australian Cyber Security Centre (ACSC) is encouraging all Australians and organisations to take action to strengthen their cyber security posture. This year's theme, “Building our cyber safe culture", focuses on three simple but effective steps: keeping software up to date, using strong and unique passphrases, and enabling multi-factor authentication (MFA) on all accounts. For cyber security professionals and organisational leaders, the ACSC will spotlight four key focus areas throughout October: event logging, legacy technology, supply chain and third-party risk, and quantum readiness. These topics aim to help organisations improve resilience and better protect critical systems and data. As Cyber Security Awareness Month gets underway, now is a great opportunity to review your organisation's cyber security practices and ensure the fundamentals are in place to reduce cyber risk. Citrix confirms two NetScaler RCE zero-days exploited in attacks Date: 2026-09-27 Author: Bleeping Computer [See AUSCERT bulletin: https://portal.auscert.org.au/bulletins/ESB-2026.11691/] Citrix has confirmed that two critical NetScaler remote code execution vulnerabilities, tracked as CVE-2026-88771 and CVE-2026-88772, are being exploited in attacks and that it has released security updates to fix the flaws. The vulnerabilities are the same zero-days that cybersecurity researchers, IT providers, and national cybersecurity agencies began privately warning organizations about over the weekend. Cisco Warns of Attackers Exploiting Critical Authentication Bypass in SD-WAN Manager Date: 2026-09-30 Author: The Hacker News [AUSCERT has informed the affected members via Critical MSINs] [Please see AUSCERT bulletin: https://portal.auscert.org.au/bulletins/ESB-2026.11917/] Attackers are exploiting a new critical zero-day flaw in Cisco Catalyst SD-WAN Manager, the system companies use to manage their Cisco SD-WAN networks, Cisco said in an advisory on September 30. The flaw, CVE-2026-76504, could allow a remote attacker with no login access to use the Manager's API as the admin user. Fixed releases are available, and there is no workaround. It carries a CVSS score of 9.8 out of 10. It sits in the part of the Manager's API that handles login sessions. Apple Patches CoreGraphics Flaw Possibly Exploited in Targeted Attacks Date: 2026-09-28 Author: The Hacker News [AUSCERT has published security bulletins for these Apple updates: https://portal.auscert.org.au/bulletins/ESB-2026.11802/ https://portal.auscert.org.au/bulletins/ESB-2026.11801/] Apple has released security updates to address a vulnerability in older versions of iOS, iPadOS, and macOS that it said may have been exploited in targeted attacks. The vulnerability, tracked as CVE-2026-86950, refers to an out-of-bounds write impacting the CoreGraphics component that could lead to arbitrary code execution when processing a maliciously crafted file. The iPhone maker said the issue was addressed with improved bounds checking. It credited Meta Product Security with discovering and reporting the issue. Google: Vulnerability disclosures double to 10,000 per month as AI fuels exploitation Date: 2026-10-01 Author: The Record Vulnerability disclosures doubled between January and August, reaching a new peak of 10,740 last month, Google’s Threat Intelligence Group (GTIG) said Wednesday. Total vulnerability disclosures began the year at 5,045 in January and had jumped to more than 10,000 for July and August. “We found that AI is measurably changing not just the pace of vulnerability discovery and exploitation, but also the types and typical risk profiles of vulnerabilities that are being discovered,” the researchers said. Queensland government department loses $800,000 in cyber attack – ABC News Date: 2026-09-30 Author: ABC News The Customer Services, Open Data, and Small and Family Business department lost $809,000 in public money due to an external cyber attack for financial gain. The department plays a lead role in strengthening the state government’s cyber security capabilities. No government data or sensitive information was compromised during the incident. ESB-2026.11795 – Apache Tomcat: CVSS (Max): 9.8 Apache Tomcat contains a vulnerability that could allow attackers to bypass security constraints protecting WebSocket endpoints. ESB-2026.11802 – Apple macOS Sequoia: CVSS (Max): 8.8 Apple macOS contains a CoreGraphics vulnerability that could allow arbitrary code execution via a malicious file. ESB-2026.11827 – MikroTik RouterOS: CVSS (Max): 9.8 MikroTik have provided update versions for the RouterOS. Successful exploitation of this vulnerability could allow an attacker to achieve remote code execution or cause a denial of service. ESB-2026.11900 – GitLab Community Edition (CE) and Enterprise Edition (EE): CVSS (Max): 10.0 Updated versions for GitLab Community Edition (CE) and Enterprise Edition (EE) were released on September 23, 2026. Gitlab strongly recommends that all self-managed GitLab installations be upgraded to one of these versions immediately. ESB-2026.11917 – Cisco Catalyst SD-WAN Manager: CVSS (Max): 9.8 Cisco has released software updates that address a vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote attacker to access an affected system with privileges of the admin user. Stay safe, stay patched and have a good weekend! The AUSCERT team

Learn more